9 min read • 1,845 words
Cybersecurity Threats Everyone Should Know About in the Digital Age
In today’s interconnected world, understanding cybersecurity threats is more crucial than ever. As technology advances, so do the tactics employed by cybercriminals. Phishing attacks, which are the most common form of cyber threat, target both individuals and organizations, often leading to devastating consequences. Additionally, ransomware attacks have surged by over 150% in the past year, crippling businesses and demanding hefty ransoms. With over 90% of data breaches attributed to human error, it is clear that awareness and education are vital in combating these threats.
This article will delve into the various cybersecurity threats that everyone should be aware of, including the vulnerabilities associated with IoT devices and the rise of social engineering tactics. By understanding these threats, readers will be better equipped to protect themselves and their organizations from potential cyberattacks, ensuring a safer digital experience.
Phishing Attacks
Phishing is a type of cyber attack where attackers impersonate legitimate organizations or individuals to trick victims into revealing sensitive information, such as passwords, credit card numbers, or personal identification details. This deception often occurs through emails, messages, or websites that appear trustworthy. Common forms of phishing include email phishing, spear phishing, and whaling, each targeting different groups or individuals with varying levels of sophistication.
Phishing emails and messages are meticulously crafted to deceive recipients. Attackers often use urgent language, enticing offers, or alarming notifications to provoke immediate action. For example, a phishing email may claim that your bank account is compromised and prompt you to click a link to verify your identity. The link typically leads to a fake website designed to capture your credentials.
To protect yourself from falling victim to phishing attempts, be aware of the following signs:
- Unusual sender addresses or domains that don’t match the organization.
- Generic greetings, such as “Dear Customer,” instead of your name.
- Spelling and grammatical errors in the message.
- Links that do not match the official website URL.
To avoid becoming a victim of phishing, consider these best practices:
- Always verify the sender’s email address before clicking on links.
- Hover over links to see the actual URL before clicking.
- Use two-factor authentication for added security.
- Educate yourself and others about the latest phishing tactics.
By staying informed and vigilant, you can significantly reduce the risk of falling prey to these prevalent cybersecurity threats.
Ransomware
Ransomware is a type of malicious software designed to block access to a computer system or data until a sum of money is paid. Typically, it encrypts files on the victim’s device, rendering them inaccessible. The attackers then demand a ransom, often in cryptocurrency, in exchange for the decryption key. This cybersecurity threat has evolved significantly, becoming more sophisticated and widespread over the years.
Recent statistics highlight the severity of ransomware attacks. According to cybersecurity reports, there was a staggering increase of over 150% in ransomware incidents in the past year alone. In 2022, the average ransom paid by organizations reached approximately $200,000, a significant rise from previous years. These figures underscore the urgent need for individuals and businesses to be aware of this threat.
Common methods of ransomware distribution include:
- Phishing emails that trick users into downloading malicious attachments.
- Malicious websites that exploit vulnerabilities in software.
- Remote Desktop Protocol (RDP) attacks that allow unauthorized access to systems.
If you find yourself infected with ransomware, it is crucial to take immediate action. First, disconnect the infected device from the internet to prevent further spread. Next, report the incident to law enforcement and consult with cybersecurity professionals. Additionally, restoring files from backups can mitigate the damage, provided that the backups are not also compromised. Remember, paying the ransom does not guarantee that you will regain access to your data, and it may encourage further attacks.
Malware
Malware, short for malicious software, is a significant cybersecurity threat that can take various forms, including viruses, worms, and trojans. Each type of malware has its unique characteristics and methods of operation. For instance, a virus attaches itself to clean files and spreads throughout a computer system, while a worm can replicate itself and spread independently across networks. Trojans, on the other hand, disguise themselves as legitimate software to trick users into installing them, allowing attackers to gain unauthorized access to systems.
Malware can infiltrate systems through several vectors. Common methods include phishing emails, malicious downloads, and compromised websites. Once a user clicks on a malicious link or downloads infected software, the malware can execute its payload, leading to severe consequences. For example, ransomware, a type of malware, encrypts files on a victim’s system and demands payment for their release, causing significant disruption to both personal and organizational data.
The impact of malware on data can be devastating. Personal data, such as financial information and passwords, can be stolen, leading to identity theft. For organizations, malware can result in data breaches, financial losses, and reputational damage. A single malware infection can compromise an entire network, affecting thousands of users.
To prevent malware infections, individuals and organizations should adopt several strategies:
- Install reputable antivirus software and keep it updated.
- Regularly update operating systems and applications to patch vulnerabilities.
- Educate users about recognizing phishing attempts and suspicious links.
- Implement firewalls to monitor and control incoming and outgoing network traffic.
By understanding the various types of malware and employing effective prevention strategies, individuals and organizations can significantly reduce their risk of falling victim to these cybersecurity threats.
Social Engineering
Social engineering is a manipulation technique that exploits human psychology to gain confidential information, access, or valuables. Unlike traditional hacking methods that rely on technical skills, social engineering targets the human element, making it a significant cybersecurity threat. Attackers use various techniques to deceive individuals into divulging sensitive information, often leveraging trust and authority.
Common techniques of social engineering include:
- Phishing: Sending fraudulent emails that appear legitimate to trick users into providing personal information.
- Pretexting: Creating a fabricated scenario to obtain information from the target.
- Baiting: Offering something enticing to lure victims into a trap.
- Tailgating: Gaining physical access to restricted areas by following someone with authorized access.
Examples of social engineering attacks are abundant in the digital age. For instance, a phishing email may appear to be from a trusted bank, urging the recipient to verify their account details. Another example is a phone call from someone pretending to be an IT support technician, requesting login credentials to resolve a supposed issue.
Attackers often employ psychological tactics such as urgency, fear, and authority. By creating a sense of urgency, they compel victims to act quickly without thinking critically. Recognizing these tactics is crucial for defense. To protect against social engineering, individuals should:
- Be skeptical of unsolicited communications.
- Verify identities before sharing information.
- Educate themselves and others about common social engineering tactics.
- Implement two-factor authentication for added security.
By understanding social engineering and its techniques, individuals can better defend themselves against these pervasive cybersecurity threats.
Data Breaches
A data breach occurs when unauthorized individuals gain access to sensitive, protected, or confidential data. This can include personal information such as Social Security numbers, credit card details, or health records. The implications of a data breach can be severe, leading to identity theft, financial loss, and damage to an organization’s reputation. In the digital age, where information is often stored online, the risk of data breaches has become a significant concern for individuals and businesses alike.
High-profile data breaches have made headlines in recent years, highlighting the vulnerabilities that exist in our digital infrastructure. For instance, the Equifax breach in 2017 exposed the personal data of approximately 147 million people. The consequences were far-reaching, resulting in lawsuits, regulatory scrutiny, and a loss of consumer trust. Similarly, the Yahoo data breaches, which affected all 3 billion user accounts, demonstrated how even large companies can fall victim to cyberattacks.
Common causes of data breaches include:
- Weak passwords and poor authentication practices
- Phishing attacks that trick users into revealing sensitive information
- Malware that infiltrates systems to steal data
- Insider threats from employees or contractors
To protect personal information from breaches, individuals should take proactive measures. This includes using strong, unique passwords for different accounts, enabling two-factor authentication, regularly updating software, and being cautious of suspicious emails or links. By staying informed about cybersecurity threats and implementing protective strategies, individuals can significantly reduce their risk of falling victim to data breaches.
IoT Vulnerabilities
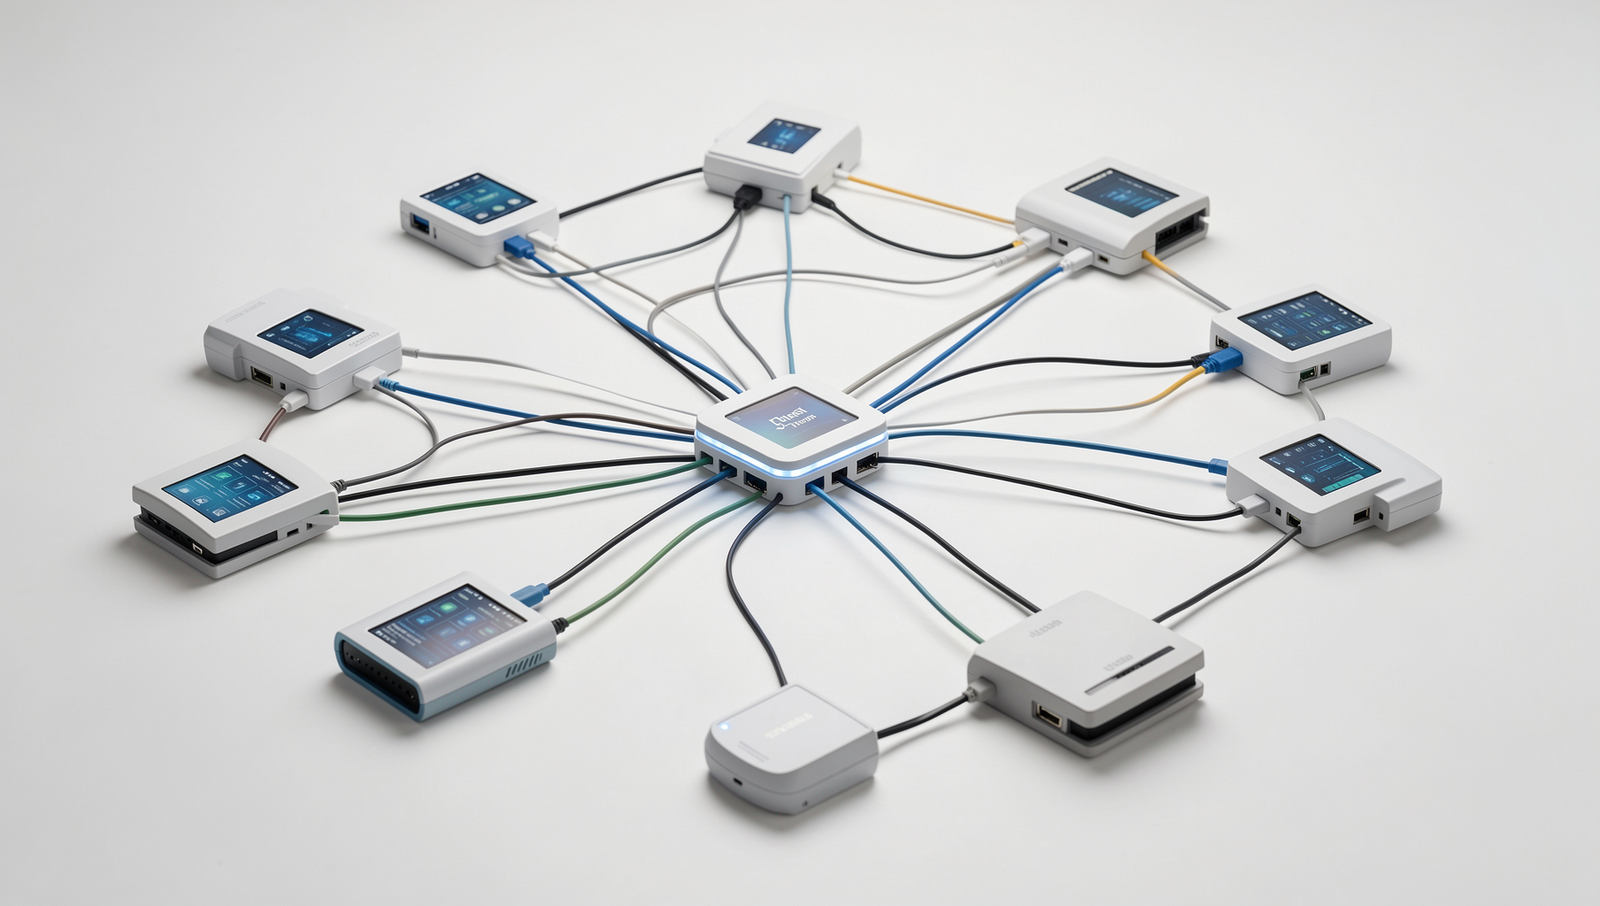
The Internet of Things (IoT) refers to the interconnected network of devices that communicate and exchange data over the internet. This technology has seen exponential growth in recent years, with millions of devices ranging from smart home appliances to wearable fitness trackers. As our reliance on these devices increases, so do the cybersecurity threats associated with them. Many IoT devices are designed with convenience in mind, often at the expense of security.
Common security flaws in IoT devices include:
- Weak or default passwords that are easy for hackers to guess.
- Lack of encryption for data transmitted between devices.
- Infrequent software updates, leaving devices vulnerable to known exploits.
- Unsecured network connections that can be easily intercepted.
The potential risks associated with unsecured IoT devices are significant. Cybercriminals can exploit these vulnerabilities to gain unauthorized access to personal information, spy on users, or even take control of devices. For example, a compromised smart camera could provide a hacker with a live feed of your home, while a hacked thermostat could be manipulated to cause extreme temperature fluctuations, potentially damaging your property.
To secure IoT devices in your home, consider the following tips:
- Change default passwords to strong, unique ones for each device.
- Regularly update device firmware to patch security vulnerabilities.
- Use a separate Wi-Fi network for IoT devices to limit exposure.
- Disable features that are not in use, such as remote access.
By taking these precautions, you can significantly reduce the cybersecurity threats posed by IoT devices in your daily life.
Conclusion
In today’s digital age, understanding cybersecurity threats is essential for individuals and organizations alike. As technology continues to evolve, so do the tactics employed by cybercriminals. From phishing scams to ransomware attacks, the landscape of cybersecurity threats is constantly changing, making it crucial to stay informed. By recognizing these threats, individuals can take proactive measures to protect their personal information and sensitive data. Organizations, on the other hand, can implement robust security protocols to safeguard their assets and maintain customer trust.
Moving forward, it is vital to prioritize cybersecurity education and awareness. Regular training sessions can equip employees with the knowledge to identify potential threats and respond effectively. Additionally, investing in advanced security technologies can help mitigate risks associated with cybersecurity threats. By fostering a culture of security and vigilance, we can collectively enhance our defenses against the ever-evolving landscape of cyber threats, ensuring a safer digital environment for everyone.
Frequently Asked Questions